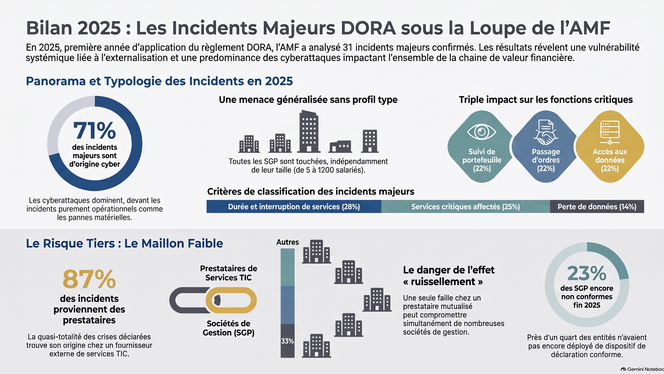
En 2025, première année d’application du règlement DORA, les Sociétés de Gestion de Portefeuille (SGP) ont confirmé 31 incidents TIC majeurs. Les cyberattaques (71 %) et le risque tiers (87 %) constituent les principales menaces, touchant prioritairement la sécurité des données et les fonctions critiques (PMS, OMS).
L'AMF relève des faiblesses persistantes : retard de conformité des PME et difficultés contractuelles face aux géants informatiques. En 2026, l'AMF fera de la résilience numérique et du contrôle de la chaîne d'approvisionnement ses priorités de supervision pour préserver la stabilité financière.
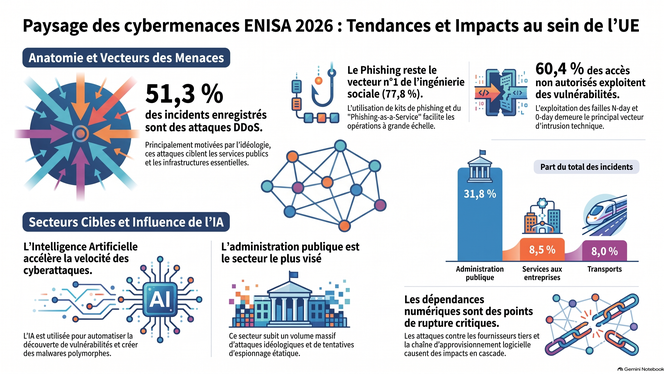
Le rapport de l’ENISA détaille l’évolution des cybermenaces dans l’UE et leurs implications (conformité NIS2, DORA) pour le secteur financier.
En 2025, les attaques sont dominées par les DDoS (51,3 %) et les accès non autorisés (39,5 %), portés par des motivations idéologiques, financières et de cyberespionnage. L’exploitation des vulnérabilités, le phishing sophistiqué (PhaaS, ClickFix) et les menaces internes constituent les principaux vecteurs d’intrusion.
Cible prioritaire subissant la pression des ransomwares et des risques liés aux tiers, le secteur bancaire voit sa résilience éprouvée. Enfin, l’intégration de l’IA accélère la vélocité des attaques, préfigurant pour 2026 une automatisation accrue de la kill chain.
This study analyzes ransomware negotiations through a social psychological lens, identifying three phases and distinct negotiation strategies. It offers practical insights for organizations to enhance resilience by understanding threat actor tactics and tailoring response protocols for effective negotiation.
This study analyzes financial risk management in digital-only banking using quantitative methods. Phishing (35%) and ransomware (20%) cause major financial losses. Basel III compliance reduces fraud risks, while AI-driven fraud monitoring has inefficiencies. Regulatory enforcement improves fraud prevention by 1.90%, highlighting the need for stronger cybersecurity and regulatory measures.
Examines the relationship between #crime and #insurance, with a focus on the role of #governance, #riskassessment and #riskmanagement, #crimeprevention, #securitytechnology, #behavioraleconomics, #theft, #kidnap and #hijack for ransom, #fraud, and #ransomware. It analyzes five case studies to identify a co-evolutionary process in which #insurers collaborate with insureds, governments, and #thirdparty to #mitigaterisk, particularly when criminal innovations destabilize the #insurancemarket.
"This paper analyzes how governments support insurance markets to maintain insurability and limit risks to society. We propose a new conceptual framework grouping government interventions into three dimensions: regulation of risky activity, public investment in risk reduction, and co-insurance."
"We propose a new conceptual framework grouping government interventions into three dimensions: regulation of risky activity, public investment in risk reduction, and co-insurance."
"As businesses improved their resilience, cybercriminals adapted and ransoms escalated, calling insurability into question. Yet there remains little appetite for imposing restrictive conditionality in this highly competitive market. Instead, insurers have turned to governments to contain criminal threats and cushion catastrophic losses."